Graduate from
prototype → production.
Plaza is the pre-Vanta for security and Vercel-class deploys — all in your own AWS account, with GCP and Azure next. You keep the keys and the access. Start free. Graduate to corporate controls and continuous compliance only when your business needs them.
Four floors. Graduate when your business is ready.
Security is table stakes at L0. L1 hardens your product. L2 covers your company. L3 manages the audit. Larger teams: ask us about Enterprise.
Compliance Pro
Continuous evidence collection and audit management. Vanta / Drata–class, without the standalone SaaS tax.
Five hours before the auditor. Every one of these would take a week.
Not the easy stuff. The controls that stop a SOC 2 report cold when the evidence isn't already running.
Built in. Not bolted on.
Secure by Default
Private subnets, encryption at rest & in transit, zero-trust networking. Configured before you write a line of code.
Infrastructure Provisioning
Multi-tier AWS account structures, VPCs, security groups, IAM roles — provisioned with OIDC. No long-lived credentials.
CI/CD Pipelines
develop → test → staging → prod. Branch protection, OIDC-based deploys, CloudFront invalidations built in.
Multi-Environment
Separate tier accounts for frontend, backend, data — each with isolated boundaries and environment-specific config.
Continuous Auditing
Compliance checks against SOC 2, NIST, ISO 27001. Evidence collection and risk registry for audit readiness.
Policy Management
IAM policies, SCPs, security guardrails — generated, version-controlled, and tracked with full audit history.
Connect in fifteen minutes. Harden one card at a time.
Connect your cloud
Deploy one CloudFormation stack in your AWS account. Plaza assumes its role with an external ID, so no access keys are stored. Guided cards then build your accounts, VPCs and Transit Gateway.
Walk the path
Complete guided security cards — each hardens your architecture or CI/CD and counts toward SOC 2, ISO 27001 and NIST readiness.
Ship with confidence
Push code through the GitHub Actions workflows Plaza generates. Deploys authenticate with OIDC — no long-lived keys — and land in your CloudTrail.
Cloud access for AI agents, tied to a human.
Plaza AIM gives each AI agent its own identity. A person hands it work from the project, signs what it may do, and can stop it at any time. It is in development; the screens below are design previews.
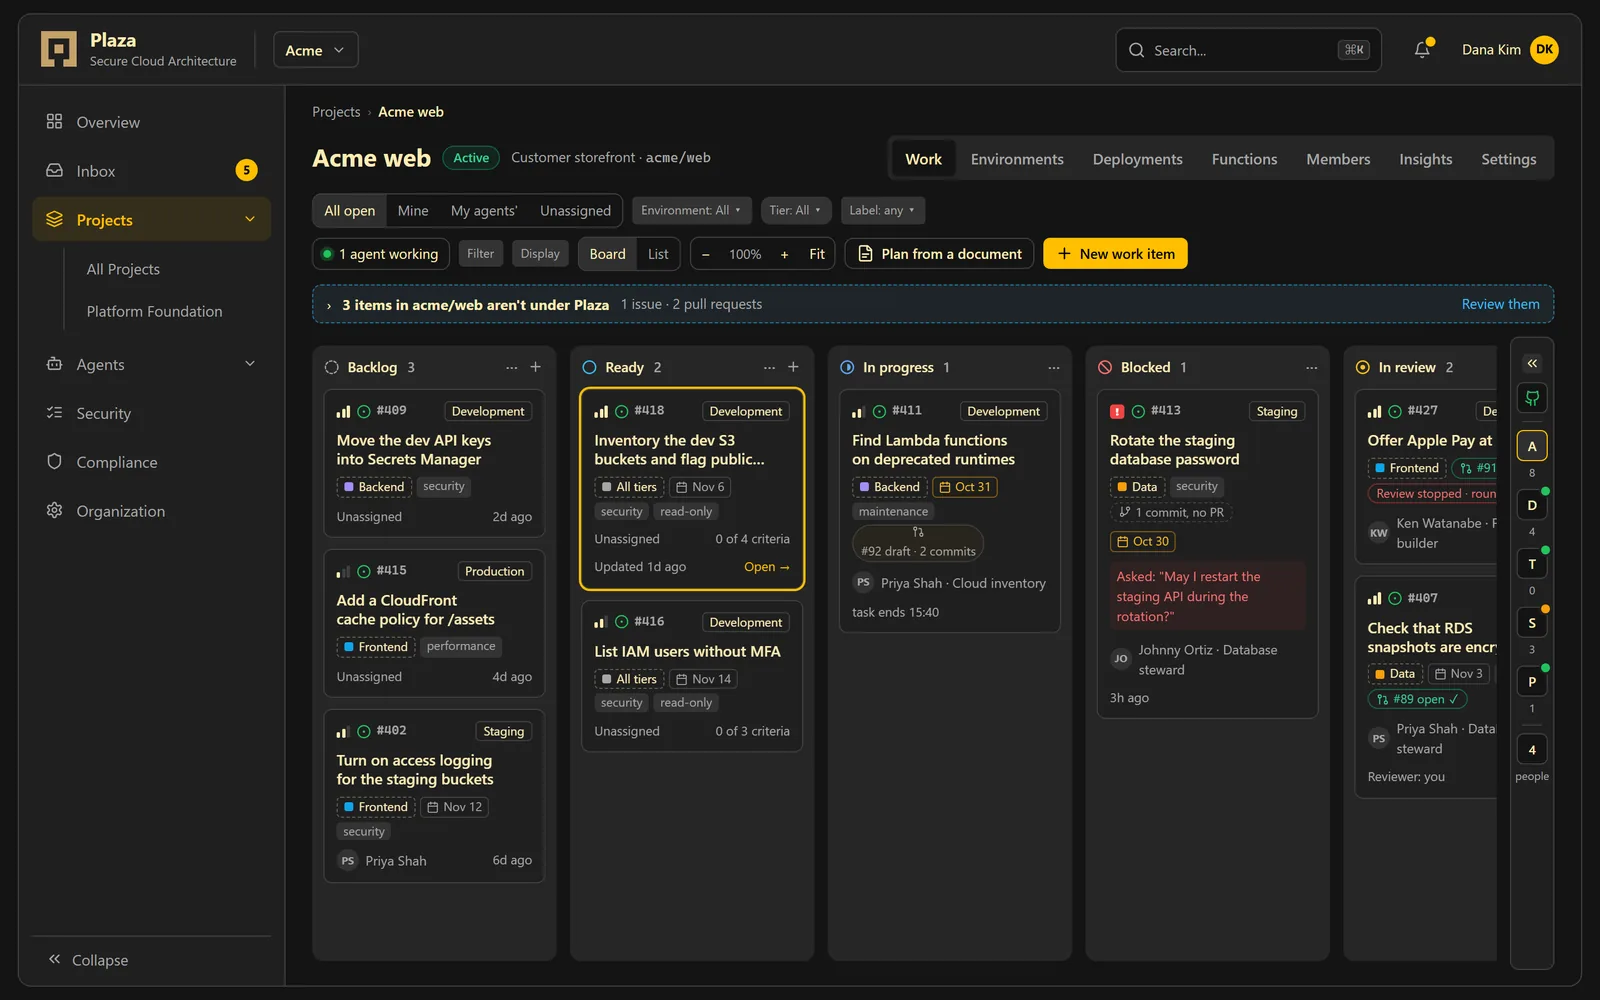
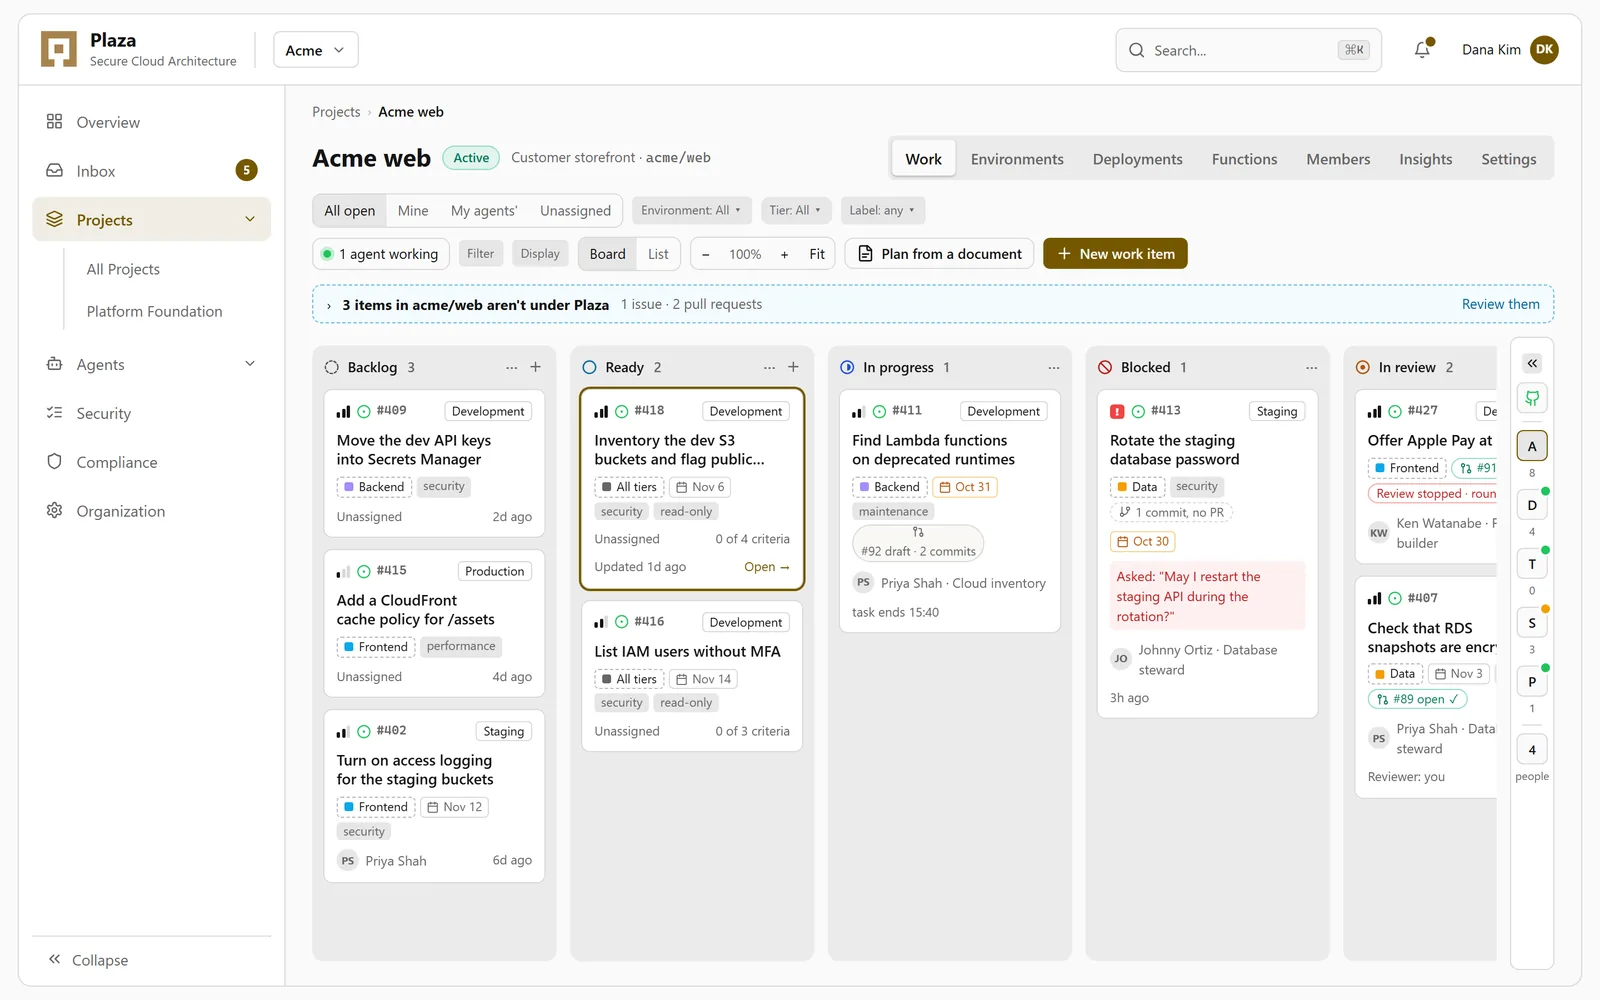
FIG. 02 — Design preview with demo data. Not available yet; details will change.
Work starts from the project
Open an issue on your project's board and see its scope and acceptance criteria before any agent touches it.
You sign what it may do
The environment, how long it may run, its budget, and what it may reach outside the project, on one page, signed with your passkey.
Short-lived, scoped access
The agent gets credentials for that task only. When its budget runs out it stops and asks you, and an emergency stop is always one click away.
Software bills of materials, built by agents
A signed SBOM for every project and the infrastructure it runs on. Agents read your code, your build and what is actually deployed, then tell you which published advisories really affect you. A person approves every "not affected" call.
Every feature and its status